
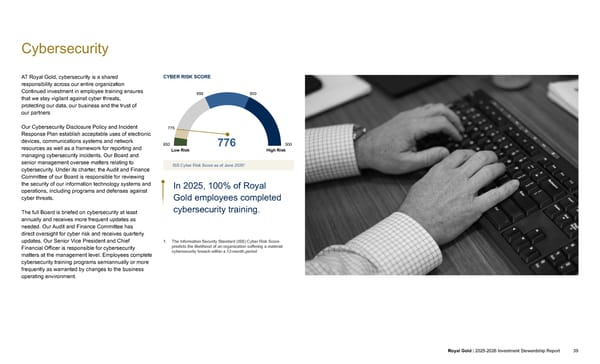
Cybersecurity AT Royal Gold, cybersecurity is a shared responsibility across our entire organization Continued investment in employee training ensures that we stay vigilant against cyber threats, protecting our data, our business and the trust of our partners Our Cybersecurity Disclosure Policy and Incident Response Plan establish acceptable uses of electronic devices, communications systems and network resources as well as a framework for reporting and managing cybersecurity incidents. Our Board and senior management oversee matters relating to cybersecurity. Under its charter, the Audit and Finance Committee of our Board is responsible for reviewing the security of our information technology systems and operations, including programs and defenses against cyber threats. The full Board is briefed on cybersecurity at least annually and receives more frequent updates as needed. Our Audit and Finance Committee has direct oversight for cyber risk and receives quarterly updates. Our Senior Vice President and Chief Financial Officer is responsible for cybersecurity matters at the management level. Employees complete cybersecurity training programs semiannually or more frequently as warranted by changes to the business operating environment. CYBER RISK SCORE Low Risk High Risk ISS Cyber Risk Score as of June 2026 1 In 2025, 100% of Royal Gold employees completed cybersecurity training. INTRODUCTION ABOUT ROYAL GOLD GOVERNANCE OUR PEOPLE OPERATORS AND COMMUNITIES INVESTMENT STEWARDSHIP APPENDICES Royal Gold | 2025-2026 Investment Stewardship Report 39 1. The Information Security Standard (ISS) Cyber Risk Score predicts the likelihood of an organization suffering a material cybersecurity breach within a 12-month period
 2025–2026 Investment Stewardship Report Page 38 Page 40